Skill
Project Handoff
Give a teammate the decisions, files, and next steps they need to continue your project.
Technical format: Tool
Package approved local files with a byte-integrity manifest, without sending them.
Create one ZIP from an explicitly approved allowlist of local files. Include selected editable/final assets, SHA-256 digests and declared credits, licenses, accessibility notes, owner, limits and next action.
A standalone Python 3.11+ CLI/library on a POSIX host with descriptor-relative no-follow operations and same-filesystem hard links. No AI host, provider or extra package is needed.
Works on its own: A native CLI/library with no synthetic SKILL wrapper, account, provider or required sibling capability. Nothing is uploaded, sent, extracted or executed.
Natural stop: Stop after preview unless the current fingerprint is explicitly approved. Build and verify then stop; a changed plan/file/destination requires a fresh preview, and existing output is refused.
A fictional repair-club delivery ZIP with selected assets, checksums and explicit declarations.
Fictional illustration, not a result from your task or measured user evidence.
Default total payload is 64 MiB, with a 512 MiB hard maximum and at most 128 files. Metadata has a separate 256 KiB bound. Checksums establish byte integrity against a trusted digest, not rights, accessibility, authority or recipient receipt. This is not encryption, a digital signature, BagIt or RO-Crate.
Skill
Give a teammate the decisions, files, and next steps they need to continue your project.
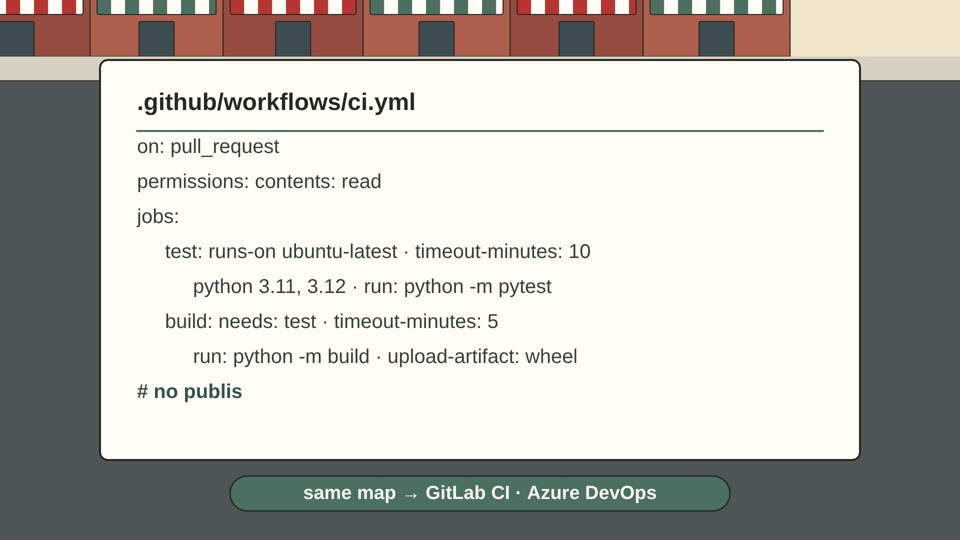
Sources to compare or explore alongside this capability. A listing does not imply an integration, partnership or endorsement.
The existing Python standard library writes and reads stored ZIP entries. Delivery Packager adds bounded allowlists, declarations and approval binding.
Difference: Uses the caller’s existing Python standard-library engine. Delivery Packager adds approval binding, bounded allowlists and declarations; no CPython implementation is vendored.
Reviewed
Choose this for creating or validating BagIt directory packages. No bagit-python dependency or interoperability is implemented here.
Difference: No code copied or installed; project metadata declares Public Domain, not an adoption or legal clearance claim.
Reviewed
Separates payload bytes and descriptive metadata with checksums. This package is a small ZIP delivery contract, not a BagIt implementation.
Difference: No specification text or implementation copied; no conformance claim.
Reviewed
Research-data metadata interchange may be useful for a future explicit export. This archive does not implement the RO-Crate format.
Difference: Research only; no specification text or code copied.
Reviewed